
Client Confidentiality, Data Rules & AI Tool Governance
A consultant uploads a messy client spreadsheet into a public AI tool to “just clean it quickly.” The output is useful, the deadline is met - and the firm may have just exposed confidential strategy, customer data and regulated information in one careless prompt.
Client confidentiality used to mean locked rooms, clean desks and secure email. In 2026, it also means prompt hygiene, data minimisation, vendor controls and knowing exactly what must never enter an AI system.
- Client confidentiality means protecting client information from unauthorised access, use, disclosure or retention.
- Classify data before using it: public, internal, confidential, restricted or regulated personal data.
- The safest AI rule: never paste client-identifiable, personal, proprietary or non-public data into an unapproved public AI tool.
- Good governance balances three things: business usefulness, legal compliance and security risk.
- Use the “C.L.E.A.N.” test: Consent, Least data, Environment, Approval, No retention.
- India-specific anchor: the Digital Personal Data Protection Act, 2023 defines personal data and puts duties on entities processing it.
- Interview answer structure: classify the data, map the rule, choose the safe tool, set controls, monitor usage.
Big Picture: Confidentiality Is Now a Workflow, Not a Policy PDF
The old mental model was “don’t leak the deck.” The modern model is sharper: every time data moves - from client email to analyst laptop to cloud drive to AI prompt to final recommendation - confidentiality must travel with it.
Core Explanation: The Three Layers You Must Always Separate
Most candidates confuse three related but different ideas: confidentiality, data rules and AI tool governance. Keep them separate and your answer immediately sounds structured.
Layer 1: Client Confidentiality
This is the professional duty. If a client shares pricing, margins, org charts, customer lists, acquisition plans, product roadmaps or internal emails, you do not disclose or misuse them - even accidentally.
In consulting and business roles, confidential information typically includes:
Layer 2: Data Rules
Data rules are the legal, regulatory and contractual requirements that govern collection, storage, processing, transfer, deletion and disclosure. For an Indian business context, the important idea is that personal data is not “just another dataset.” Under India’s Digital Personal Data Protection Act, 2023, personal data means “any data about an individual who is identifiable by or in relation to such data”.
For a student, the practical rule is simple: if a dataset can identify a person directly or indirectly, treat it as regulated unless someone senior confirms otherwise.
Layer 3: AI Tool Governance
AI tool governance decides which AI tools can be used, for which tasks, with which data, under what controls. The issue is not “AI is risky.” The issue is that AI changes the route data takes. A normal spreadsheet may become a prompt, a model input, a training artefact, a log, or a vendor-retained record.
The C.L.E.A.N. Test for Safe AI Use
When you are unsure whether you can use a dataset in an AI tool, run this five-part test. It is practical enough for project work and clear enough for interviews.
Unsafe prompt: “Analyse this client sales file and identify which customers are likely to churn,” followed by a raw upload containing names, phone numbers and purchase history. Safer prompt: “Here is a synthetic version of a B2B sales dataset with anonymised customer IDs and banded revenue. Suggest churn drivers and analysis steps.” The strategic point: you can still get thinking support without exposing client-identifiable data.
Definitions You Should Be Able to Say in One Breath
- Confidentiality: “Preserving authorized restrictions on information access and disclosure, including means for protecting personal privacy and proprietary information” (NIST Glossary).
- Personal data: “Any data about an individual who is identifiable by or in relation to such data”.
- AI risk management: The process of governing, mapping, measuring and managing AI risks, reflected in the NIST AI Risk Management Framework.
What to Track: Governance Metrics That Are Real, Not Vague Intentions
If you say “we will monitor compliance,” an interviewer may ask, “How?” These six metrics make your governance answer operational.
Case Study: RBI Card Tokenisation - Confidentiality by Design
India’s card tokenisation framework shows how sensitive data can be protected by redesigning the system so merchants do not need to store actual card details.
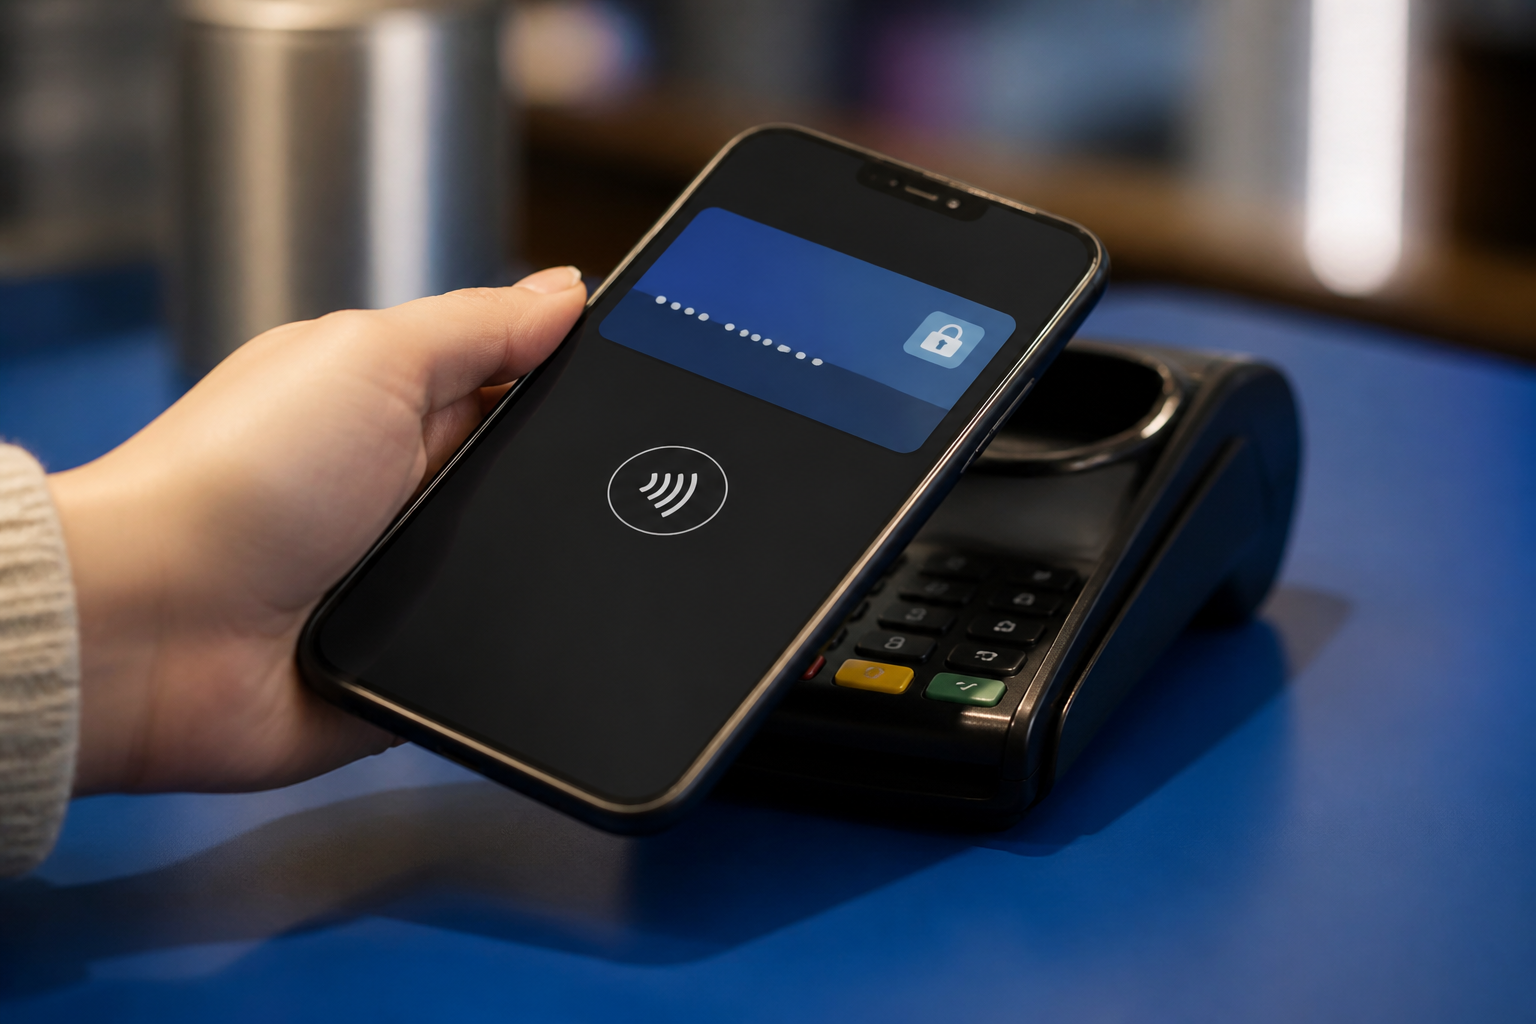
The situation was familiar to every digital commerce business: card payments require speed and convenience, but raw card details are highly sensitive. The more places card data sits - merchant databases, apps, checkout systems, vendor platforms - the more points of failure exist.
The strategic move was tokenisation. In card tokenisation, the actual card number is replaced with a token that can be used in a specific payment context, while the real card details remain protected within authorised systems. The Reserve Bank of India explains tokenisation for card transactions in its official FAQ on card tokenisation.
The lesson for client confidentiality is powerful: do not rely only on employee discipline. Redesign the workflow so the risky data is not broadly visible in the first place.
The “so what” for consulting and AI governance: before asking “Can we trust people not to paste sensitive data?”, ask “Can we mask, tokenise, aggregate or simulate the data so they never need to paste it?”
How AI Changes Client Confidentiality, Data Rules & AI Tool Governance
AI does not remove confidentiality duties. It makes them harder because data can now be transformed, summarised, embedded, stored in logs, reused in workflows and exposed through prompts.
1. Prompt Inputs Become a New Data Leakage Channel
A prompt can contain client names, financial assumptions, code, contracts, HR data or deal strategy. Even if the AI output looks harmless, the input may already be a breach if the tool is not approved for that data class.
2. AI Outputs Can Recreate Sensitive Patterns
Even when names are removed, outputs may reveal patterns: “the only plant in Gujarat with this capacity,” “the client planning a price rise,” or “the acquisition target in the pharma sector.” Governance must therefore cover both inputs and outputs.
3. Tool Choice Becomes a Risk Decision
Public chatbots, enterprise AI workspaces, internal copilots and client-approved sandboxes do not carry the same risk. A good firm policy specifies which tools are approved, whether prompts are retained, whether data is used for training, who can access logs and what data classes are prohibited.
Before a consulting interview, load your own notes on this topic into NotebookLM and ask: “Create 10 interviewer questions on client confidentiality, DPDP, and AI tool governance. For each, mark what data should never be put into a public AI tool.” Do not upload real client, employer or internship data while practising.
If you want the broader consulting context, revise how AI is changing delivery models and analyst work in How AI Is Changing Consulting Roles, Pyramids & Pricing.
Interview Relevance
“You are staffed on a cost-reduction project. The client sends you employee-level productivity data and your manager asks you to use an AI tool to find patterns quickly. What checks will you do before using the tool?”
Use the phrase “approved environment” instead of just “secure tool.” It signals that you understand governance includes vendor approval, access control, retention policy, auditability and client permission.
For case interviews, this topic often appears after the business problem is framed. If your structure is weak at the start, revise Defining the Problem Before Solving It before practising confidentiality add-ons.
Common Mistake
The biggest mistake is saying, “I will anonymise the data,” as if anonymisation solves everything. It may not: combinations of location, role, transaction size or timing can still re-identify people or reveal client strategy. One-line fix: say, “I will classify the data, minimise it, use an approved environment, and escalate if re-identification or client sensitivity remains.”